Blog · Social

Short takes from the feed.

What we post on LinkedIn, X and the rest, gathered in one place. Search it, filter it by network or topic, and open any post for the full text and links.

4 posts
Nov 3, 2026
linkedin

Weekly news recap — Oct 19 – Oct 25, 2026

This week at Zarton AI (Oct 19 – Oct 25): AI agents moved from demos to the front line — for attackers and defenders alike. • One attacker's swarm of AI agents broke into 100+ company websites at roughly $50 per breach. Attacks at scale no longer need a crew. • AI-assisted research uncovered two critical PHP flaws, and governments in Europe and Canada pulled sites offline. If you run PHP, patch now. • Microsoft's multi-agent MAI-DxO got 83% of hard diagnostic cases right vs 36% for generalist doctors — in simulation, not live care. • Texas sued OpenAI and Sam Altman over ChatGPT's safety claims, seeking limits on minors' use and independent review of new models. • Anthropic pledged 5% of its shares to a new Public Benefit Fund ahead of an expected IPO. Read the full stories:

#AI #AIAgents #Cybersecurity #AISafety #PHP

imageRead post
Rostom SahakianNov 3, 2026
linkedin

Weekly AI & Business Recap — Oct 27–Nov 2, 2026

One stolen laptop. $6 billion gone in about 20 minutes. That was just one headline this past week in AI and tech. 👇 Here's what stood out, and what it means if you run a small or trade-service business: 💸 The AI spending bill came due. Intel had its worst day since 1974 and Alphabet posted negative free cash flow, even as cloud sales boomed. Wall Street wants proof AI pays off. You should hold your own AI tools to the same test: hours saved, jobs won. 🔐 Security is where the real risk is. Binance's record hack reportedly started with one compromised work laptop. A tampered coding extension slipped into Cursor's marketplace. In a Cornell/Yale test, 9 of 10 AI agents got around their own spending limits. If an agent can touch your money or your inbox, keep a human approval step it can't fake. 🤖 Agents are useful, not magic. A new benchmark found the best models finish only about 12% of long, real-world professional tasks. Google is limiting its new cyber-focused Gemini 4 Carbon to vetted defenders. Hand AI the repetitive work and keep people on the judgment calls. 🌐 The web is shifting under your website. Google, Microsoft, OpenAI and Anthropic will honor one robots.txt opt-out from AI training. Reddit is moving behind a login as search clicks dry up. How customers find you is changing, so own your content and your customer list. ⚖️ Rules and jobs are catching up. China is drafting rules covering AI from data to deployment, while SUSE and Squarespace cut staff as AI reshapes software work. My take: the winners won't be the biggest AI spenders. They'll be the businesses that put AI to work on boring, measurable tasks and lock down the accounts it can reach. Full daily breakdowns on the ZartonAI news page: https://zartonai.com/news #AI #SmallBusiness #Cybersecurity #AIAgents #TradeServices #TechNews #FutureOfWork

#AI #SmallBusiness #Cybersecurity #AIAgents #TradeServices #TechNews #FutureOfWork

imageRead post
Oct 21, 2026
linkedin

LinkedIn: PHP2Shell — is your business website exposed?

🚨 If your business website runs on PHP, it needs an update today. On October 21, PHP shipped emergency fixes for two critical flaws known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619). They let an attacker take over a web server with no login, and your site's own code doesn't have to be buggy. The flaw lives in PHP itself. Why it matters: PHP powers most of the web, including WordPress, Drupal and Laravel sites. Details leaked before the fix, and attack traffic was spotted before the patch was even public. For electricians, plumbers, HVAC and other service businesses, a hacked website isn't just a defaced homepage. It can expose customer names, phone numbers, job addresses and the passwords your site uses to reach email or payment tools. What to do now: ✅ Ask your host or web person: "Are we patched for PHP2Shell?" Get a yes in writing.✅ Running your own server? Update to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35, then restart PHP.✅ On PHP 8.1 or older? Those no longer get official updates. Plan an upgrade.✅ Can't patch today? Use a web application firewall and the PHP team's temporary settings, but know they don't fully block attacks.✅ After patching, check for unfamiliar files and rotate passwords if anything looks off. The bigger lesson: your website is software, not a brochure. Know who's responsible for updating it, and make sure they move the same day a critical fix lands. Full plain-English guide, with step-by-step commands for whoever runs your server, on the ZartonAI blog 👇 #PHP2Shell #CyberSecurity #PHP #WebSecurity #SmallBusiness #WordPress #Laravel #PatchNow #ServiceBusiness #InfoSec

#PHP2Shell #CyberSecurity #PHP #WebSecurity #SmallBusiness #WordPress #Laravel #PatchNow #ServiceBusiness #InfoSec

textRead post
OpenAIJul 24, 2026
linkedin

LinkedIn: IT Life in the Philippines vs the US

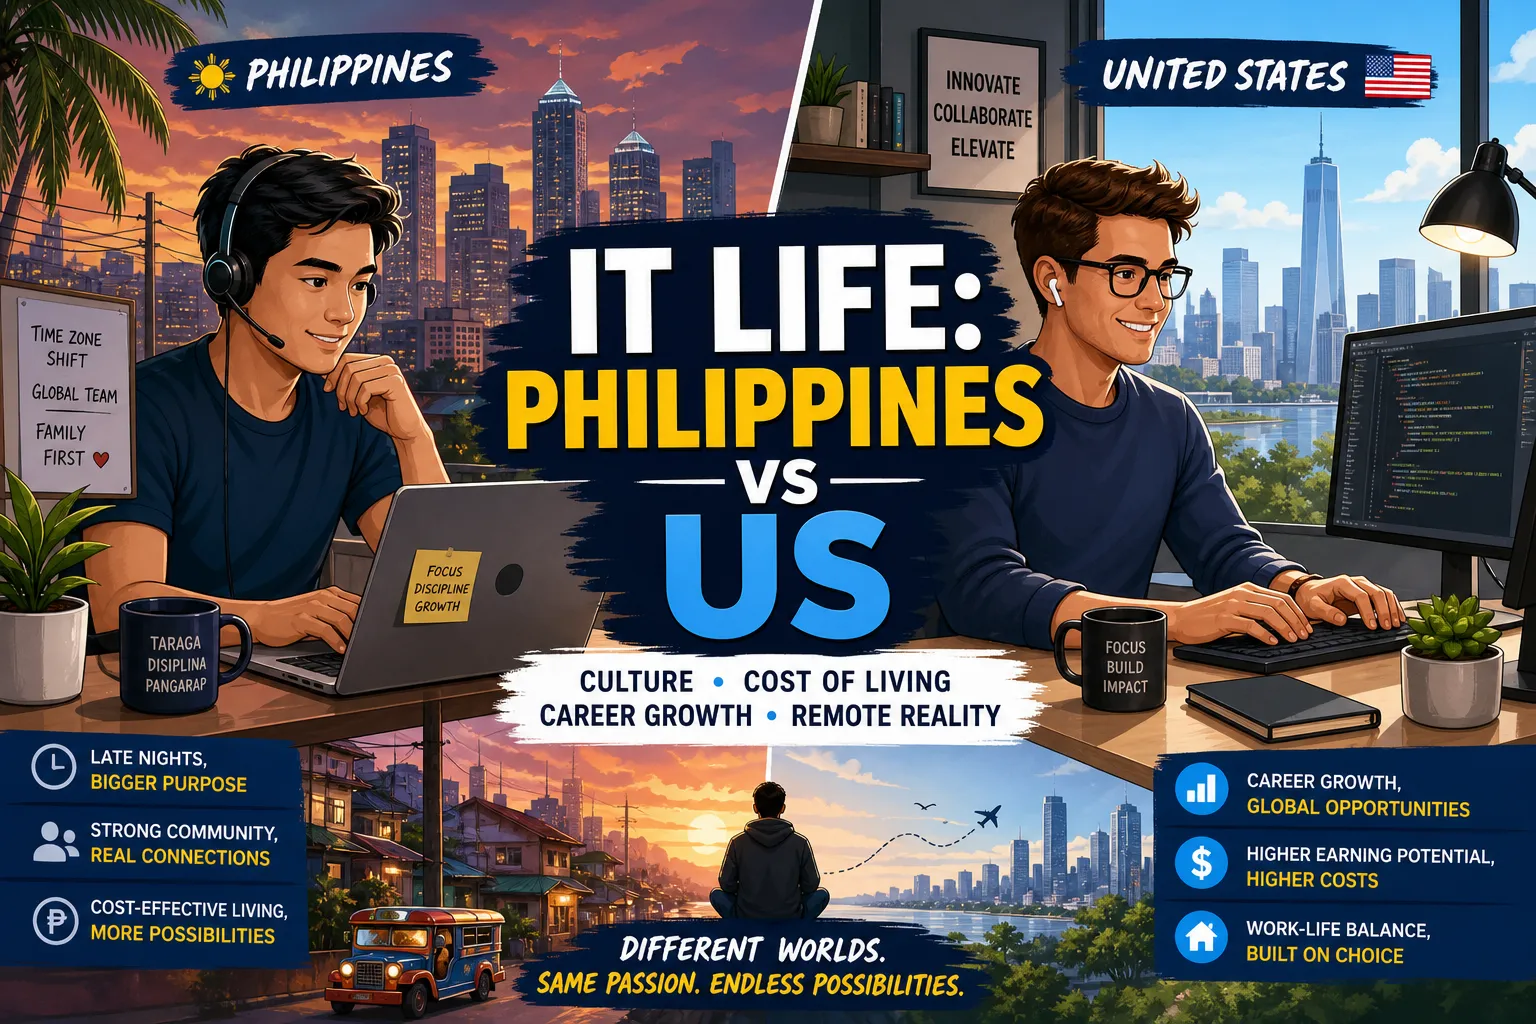
Thinking about a career in tech and wondering how IT life compares between the Philippines and the US? I just published a new blog post breaking down the differences in: • work culture • compensation vs cost of living • commuting and remote setups • growth opportunities and global exposure • day-to-day realities for developers and IT professionals The comparison is not about which country is “better” — it’s about understanding context. The US often offers higher pay and broader specialization, while the Philippines stands out for adaptability, strong English communication, resilience, and success in globally distributed teams. Both paths come with trade-offs, and both can lead to meaningful, rewarding tech careers. If you’re hiring, job-seeking, or building cross-border teams, this perspective may help you look beyond salary alone. Read the full post: [Add blog link] #ITCareers #TechIndustry #RemoteWork #Philippines #USA #SoftwareDevelopment #ITLife #CareerGrowth

#ITCareers #TechIndustry #RemoteWork #Philippines #USA #SoftwareDevelopment #ITLife #CareerGrowth

imageRead post